Every device on your network. Zero probes.
NS-Discovery builds a live asset inventory by listening to the traffic devices already broadcast on each segment where a Sensor runs. No scanning, no agents, no vendor cloud. Active probing stays off unless you turn it on. And every classification shows the evidence behind it.
- Sends nothing to printers, PLCs or medical devices
- One Linux host per segment, about an hour to install
- Nothing is ever sent to us
| Device | IP | Site | Status |
|---|---|---|---|
| 10.0.4.21 | Boston | identified | |
| 10.0.4.57 | Boston | Windows 7 | |
| 10.0.9.140 | Warehouse | new | |
| 10.0.0.2 | HQ | identified | |
| 10.0.9.33 | Warehouse | unknown |
On the Sensor: why “HP LaserJet M404”?
2 independent signals · last seen 2 min ago
mDNS_ipp._tcp “HP LaserJet M404dn”DHCPvendor class “Hewlett-Packard JetDirect”MACa0:d3:c1 → HP Inc. (context only)
Decodes 13 discovery protocols
- ARP
- DHCPv4
- mDNS
- LLMNR
- NetBIOS
- SMB Browser
- SSDP
- LLDP
- CDP
- MNDP
- PROFINET
- EtherNet/IP
- BACnet
Who it’s for
Built for networks you can’t afford to scan.
Active scanners can crash fragile equipment and agents can’t be installed on a printer. Passive discovery works on everything that talks.
Healthcare & clinics
Every device that talks shows up, including infusion pumps, imaging and unmanaged IoT, and nothing is sent to them. What the rules can’t identify is listed as unknown, not guessed. Keep an asset list your auditor can trace.
Manufacturing & OT
Inventory PLCs, HMIs and legacy controllers on isolated segments. Export files for air-gapped networks.
Offices & schools
Laptops, phones, printers, projectors and the device nobody admits to plugging in. A continuous inventory instead of a yearly spreadsheet.
MSPs
Drop a Sensor at each client site and hand over clean reports at onboarding and QBRs. Today: one Manager per client, or one Manager with users limited to chosen Sensors.
How it works
From a mirror port to an inventory you can show an auditor.
Two small programs that you run yourself. Each is a single binary with a built-in database, plus a signed recognition package and a license file.
Switch or SPAN port
Devices already announce themselves with DHCP, mDNS, LLDP and more. A mirror port shows the most; a plain access port still hears the broadcast and multicast announcements most discovery relies on.
traffic
Listens and classifies
Decodes discovery protocols, keeps evidence per device and applies reviewed rules. Packets never leave the host.
Ubuntu 22.04 / 24.04 LTS · amd64mTLS 1.3
All sites in one place
Inventory, change feed, findings and reports for every site. SSO, roles, per-site access.
On-prem or your cloud VMExplainable by design
Every answer shows its work.
A label alone is hard to trust. NS-Discovery shows the packet-level facts behind each one, so you can check it, or prove it wrong.
- Evidence, not magicEach fact is stored with its source protocol and age.
- Fixed, reviewed rulesNo black-box ML. If the evidence isn’t there, the field says “unknown”.
- Auditor-friendlyReports show the figures behind every claim, are dated, and keep a SHA-256 of their content.
FRONTDESK-07
10.0.4.57 · 18:03:73:1a:77:0e| Source | Observed | Age |
|---|---|---|
DHCP | Vendor class “MSFT 5.0”, parameter list of the Windows 7 generation | 4 min |
SMB | Browser announcement: Windows 6.1 workstation | 12 min |
MAC | 18:03:73 registered to Dell Inc. (context) | — |
SSDP | Server: “Microsoft-Windows-NT/6.1 UPnP/1.0” | 1 h |
windows_browser_announcement · first seen Oct 14 · 3 IP changes in 30 daysWhat you get
Know what changed, not just what’s there.
Change feed
New, returning and unapproved devices and new findings, sent to a webhook, e-mail or your SIEM within about a minute.
Outdated systems
Spot devices announcing an operating system past its end of support, like Windows 7 or Server 2012 R2.
IP history
Who had 10.0.4.57 last Tuesday at 3 pm? Answer incident questions by time and site.
Audit reports
Coverage tables for CIS Controls v8, NIST CSF 2.0, NIST SP 800-171 r2 3.4.1 (CMMC Level 2) and the proposed 2025 HIPAA Security Rule, with partial coverage marked. Evidence, not a certification.
SSO & roles
OpenID Connect, four roles including read-only auditor, per-site access enforced on the server.
Fits your stack
Syslog / CEF, CSV export, CLI and API. Read-only Android app (early access) for on-call checks.
The Manager
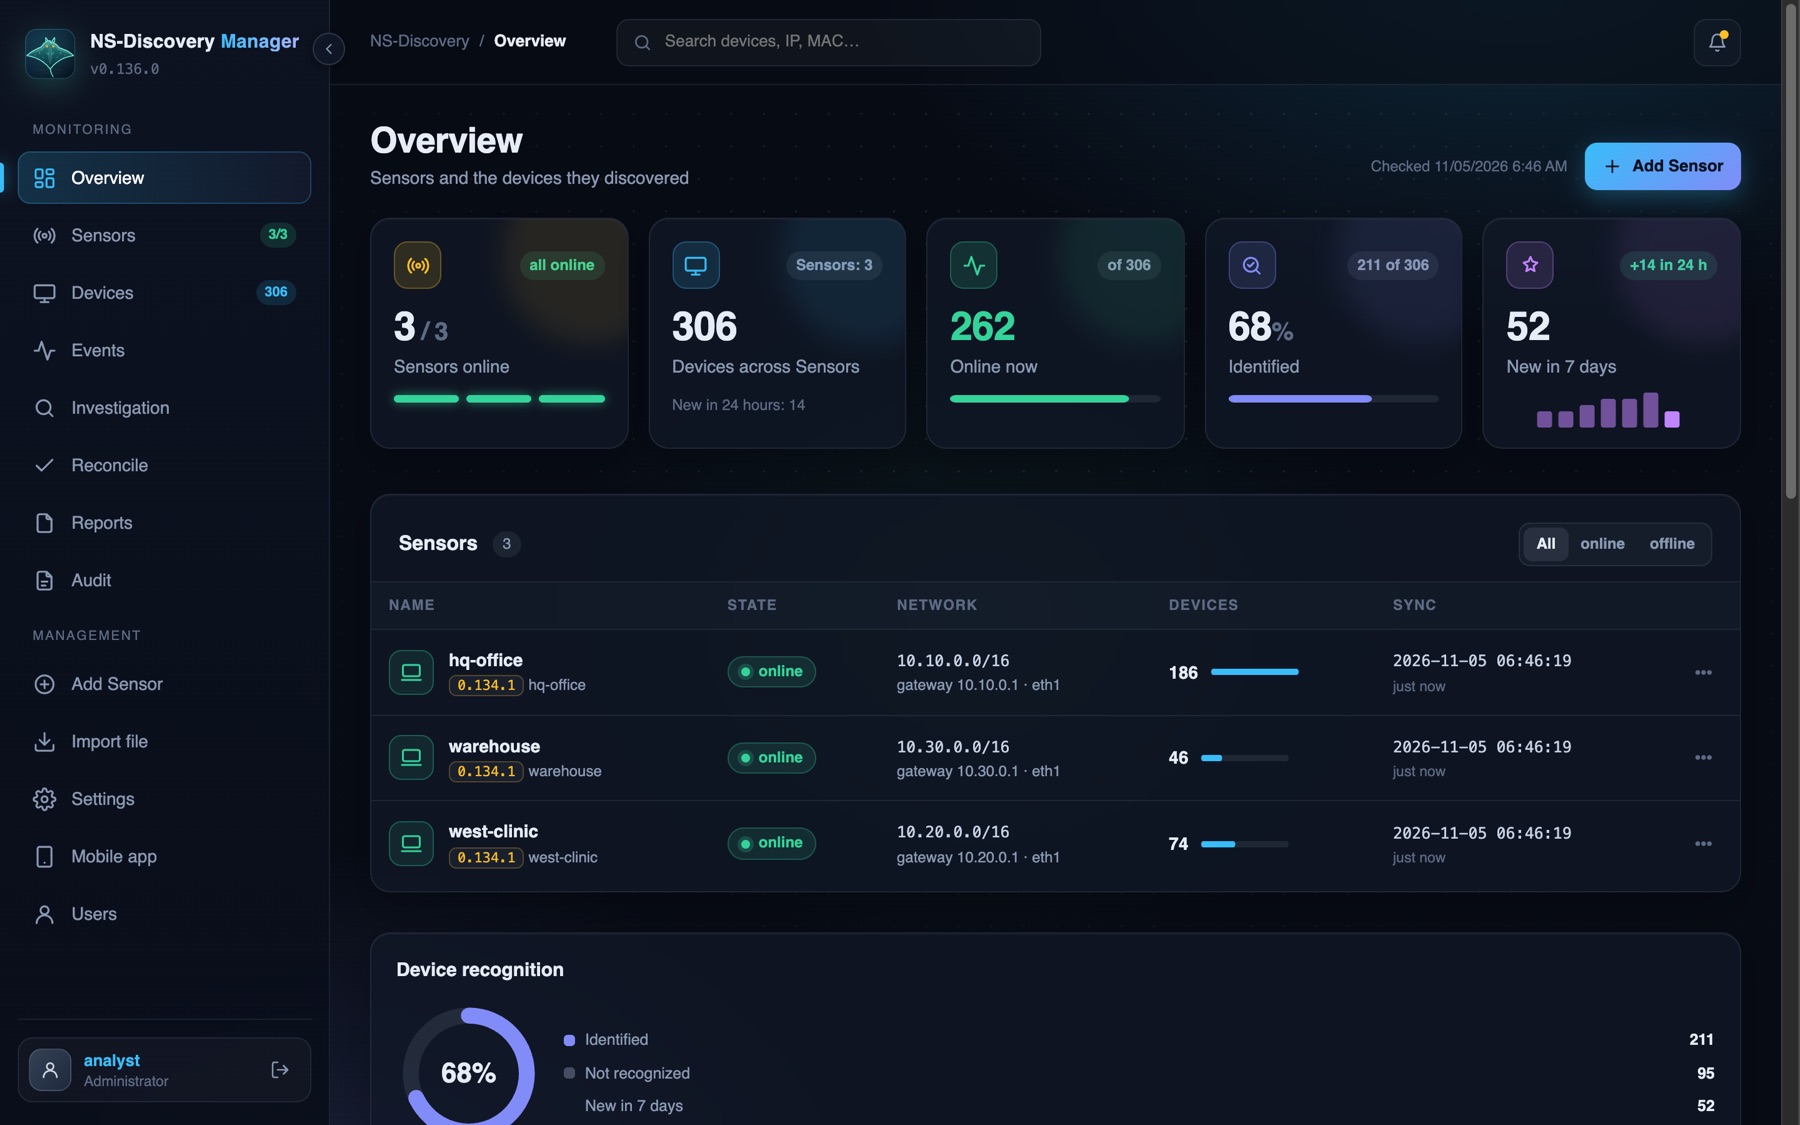
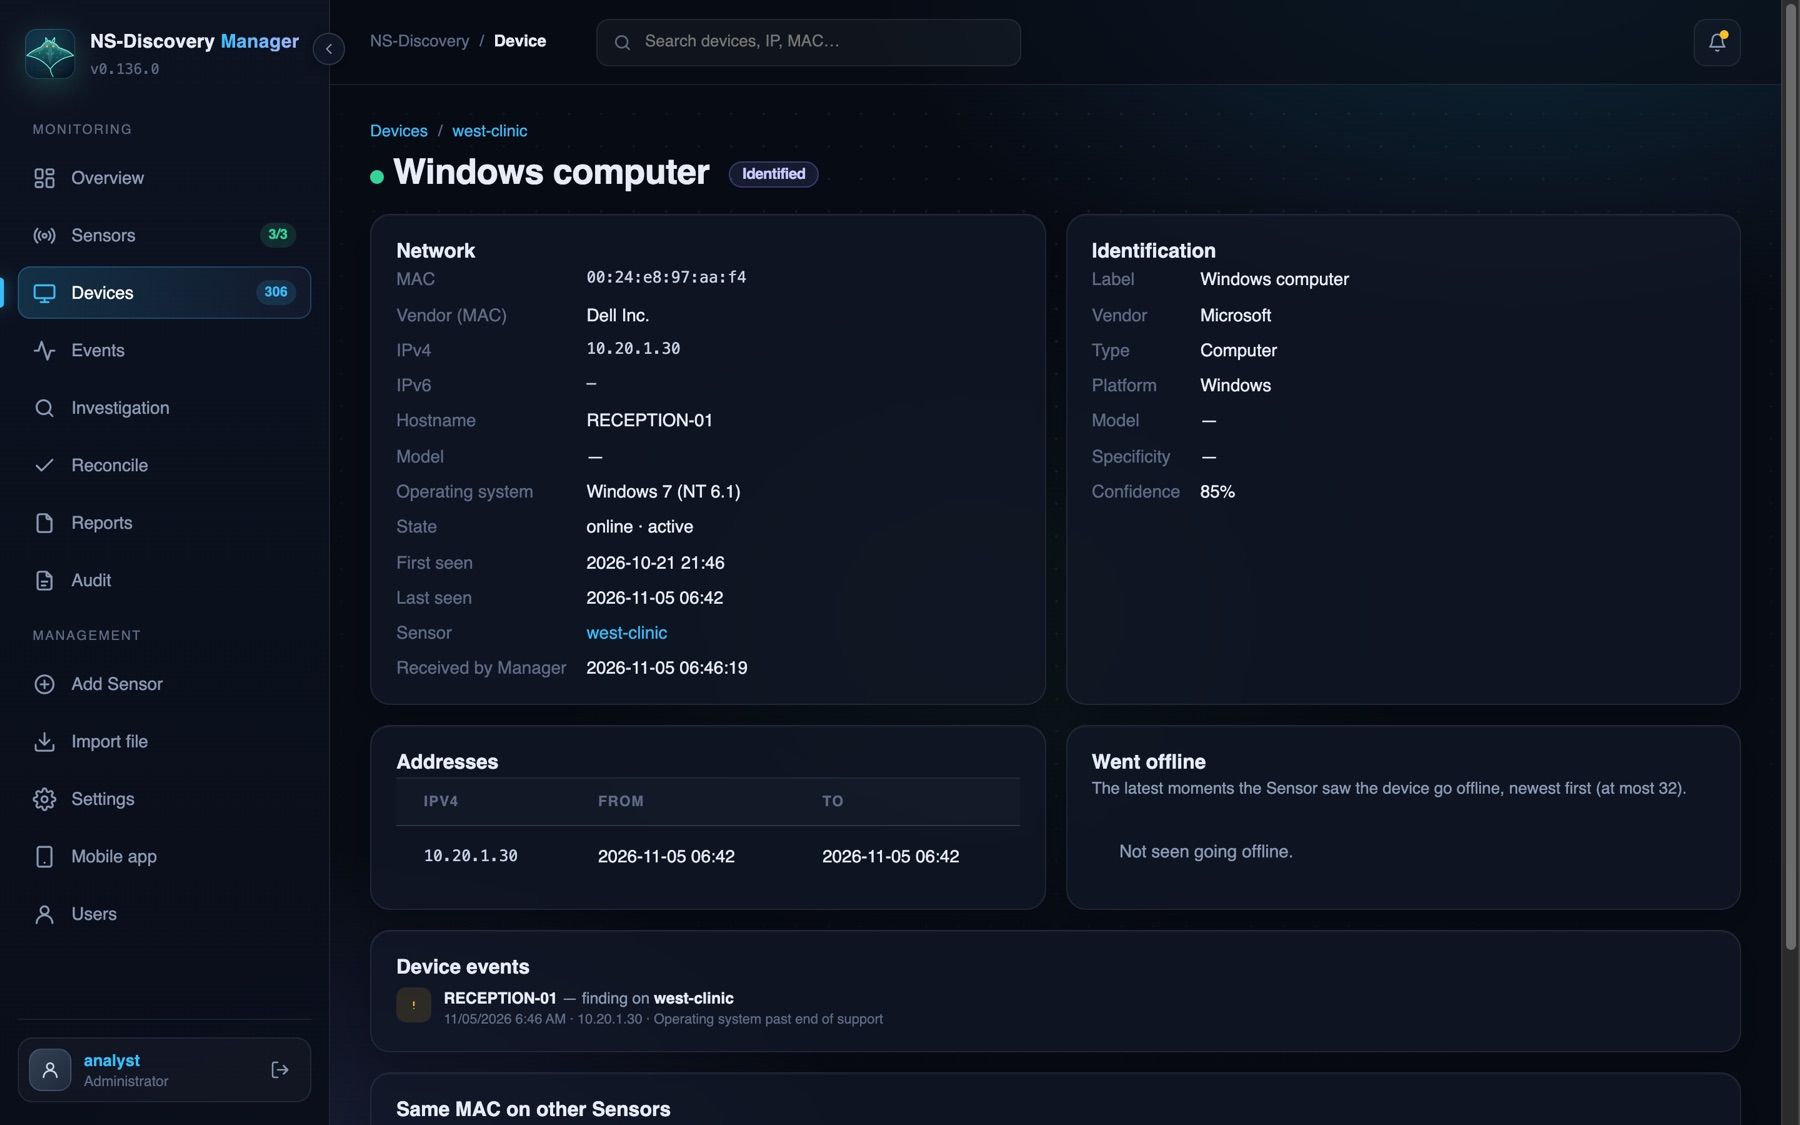
Real screens, demo network.
Three sites and about 300 synthetic devices. Every name and address is generated; no customer data.
Compared
Why passive?
| Active scanner | Endpoint agent | NS-Discovery | |
|---|---|---|---|
| Traffic it generates | Probes every host | Agent check-ins | None on monitored segmentOptional ARP discovery, off by default |
| Sees IoT, printers, OT | Partly | No | Yes, if it talks |
| Safe for fragile equipment | Risky | N/A | Yes |
| Continuous change detection | Between scans | Yes | Yes, continuously |
| Install on every device | No | Yes | No, one host per segment |
| Passwords to your hosts | Admin accounts for deep checks | Runs with admin rights on each device | None needed, none stored |
| Footprint | A server sized for the scan load | Software on every device | 65–90 MB peak memoryone small host or VM per segment |
Security
The least risky thing on your network.
A tool that maps your network shouldn’t become a way into it. Here’s exactly what it does, and what isn’t done yet.
Not done yet, and we’ll say so
- No SOC 2 report yet.
- No third-party penetration test yet. Planned.
- Packages are not signed yet; each build comes with its SHA-256.
- Live-capture throughput on Linux is not measured yet.
- We don’t host customer data, so there’s nothing of yours on our side.
Recorded office and small-network captures replayed from file through the full Sensor pipeline on an Apple M3 laptop; captures dense with discovery traffic run at about 20k frames/s. Live capture on Linux is not measured yet.
Free pilot
One segment. One week. No purchase.
We’re in early access and not selling yet. Pilots help us improve recognition. You keep the inventory and the report.
- Intro call 30 minTell us about your network. We tell you if it’s a fit.
- Install the Sensor ~1 hourA Debian package on an Ubuntu host or VM in the segment.
- Let it listen ~7 daysThe Sensor sends no discovery traffic; only its host’s own traffic goes out.
- Review together 1 hourWalk through what it found, including what it couldn’t identify.
- Keep or removeKeep the report. apt purge ns-discovery removes the Sensor and all its data.
Request a pilot
Write to us with a few lines. We aim to reply within two business days.
- Your organizationAnd whether you are a managed service provider.
- SizeRoughly how many devices and sites.
- Network typeOffice, clinic, plant, school or a mix.
Only for networks you are authorized to monitor.
FAQ
Questions IT teams ask first
Does it really send nothing?
On the segment it monitors, the Sensor only listens. It does not scan, ping or probe. Two exceptions, both under your control: an optional local ARP discovery mode that is off until an operator enables it, and the connections you configure from its host: mTLS to your own Manager and syslog to your SIEM.
What hardware do I need?
An Ubuntu 22.04 or 24.04 LTS host or VM on the segment you want to see; 2 GB of RAM is enough for a small network, and we size larger sites with you. A Debian package for Ubuntu 22.04 and 24.04 LTS on amd64; an arm64 build is available on request. A SPAN/mirror port gives the best coverage, a regular access port also works.
Where does my data go?
Nowhere outside your infrastructure. The Sensor and Manager run on your hardware or in your own cloud account. We see only what you choose to show us on a call.
How is this different from Nmap, Lansweeper or a NAC?
Scanners send traffic to every host and only see what answers. Agents need installing on each device. A NAC controls who may connect; it is not built to explain what a device is. NS-Discovery identifies devices from what they already broadcast, sends nothing to them, and keeps watching continuously.
Do we still need our vulnerability scanner?
Yes. They answer different questions. NS-Discovery shows what is on the network, including devices that appeared between scans or never answered one; your scanner checks hosts for vulnerabilities. Today you can reconcile our inventory against any CSV list of IP or MAC addresses, such as a scanner export, and see which devices the list is missing. Direct import of Tenable, Qualys and Rapid7 scan scopes is on the roadmap.
What will it cost after early access?
Pricing is not set yet, and we are not selling during early access. Pilots are free, and pilot participants hear about pricing first.
See your network as it really is.
Try it on one segment for a week. Free, with a short pilot agreement.